Compliance Dashboard
Security You Can Verify.Reliability You Can Depend On.
Every test run, every integration, every byte of data is protected by controls your security team can audit, verify and trust - across every region you operate in.
99.9%Uptime SLA Guaranteed
AES-256Encryption Always On
0Active Certifications
3 MonthsAudit Log Retention
Certifications
Security Assured.Compliance Verified.
FireFlink is independently audited against the world's most rigorous security frameworks so your team ships with confidence.
Security & Governance
Governed by Policies.Enforced by Architecture.
Our security practices, VAPT results, access controls, and audit log policies.
DP
Data Protection Officer
Responsible for overseeing FireFlink's data protection strategy and GDPR compliance.
dpo@fireflink.com
Access Control
Role-BasedAccess Matrix
Granular, auditable permissions for every role - no ambiguity about who can see or do what.
| Capability | Super Admin | Admin | User | Guest |
|---|---|---|---|---|
| License Management | Full Access | No Access | No Access | No Access |
| Create Projects | Can Create | Can Create | No Access | No Access |
| Project Inclusion | All Projects | New Projects | Assigned Projects | Assigned Projects |
| Project Removal | Cannot Be Removed | Cannot Be Removed | Can Be Removed | Can Be Removed |
| Project Access | Full Access | Full Access | Role-Based | View Only |
| User Management | Full Access | Manage Users | No Access | No Access |
| Configuration Access | Full Access | Full Access | Role-Based | View Only |
| Resource Access | Full Access | Full Access | Role-Based | View Only |
| Billing & Subscription | Full Access | No Access | No Access | No Access |
Data Governance & Privacy
Your Data.Your Control.
Choose where your data lives, who can access it and how long it is retained - enforced at the platform level.
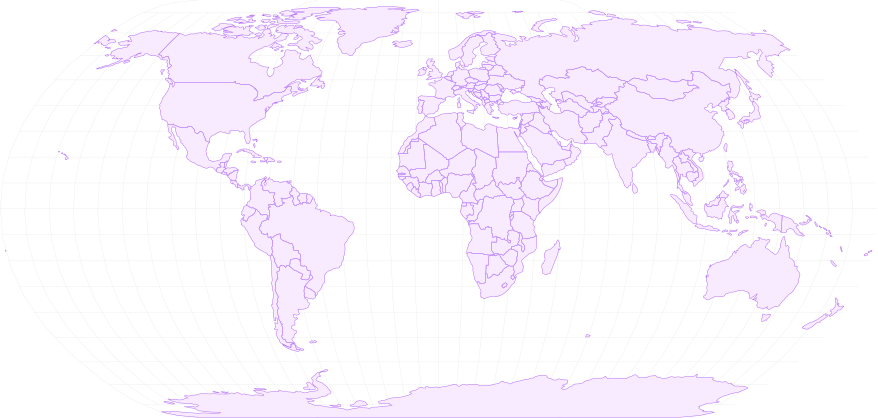
Frankfurt, Germany
St. Louis, USA
California, USA
 UAE
 India
Singapore
Automation and Device Farm
Automation
Device Farm
Policies Repository
Every Policy.Audit-Ready.
Request the policy and compliance documentation required for your audit or security review.
Policy NameAction
Uptime & Incident Transparency
No surprises.Ever.
Every incident disclosed publicly. Every outage measured. Zero spin - only facts your team can rely on.
All Regions Operational
99.9%90-day uptime
2.1savg response
0open incidents
Security Questionnaire
Explore our security, privacy and compliance standards.
Request the exact policy document your security team or auditor needs - versioned, dated and ready for review.
View Complete Security Questionnaire
Explore the full set of security and compliance questions covering infrastructure, access control, data protection, monitoring, governance, and more.